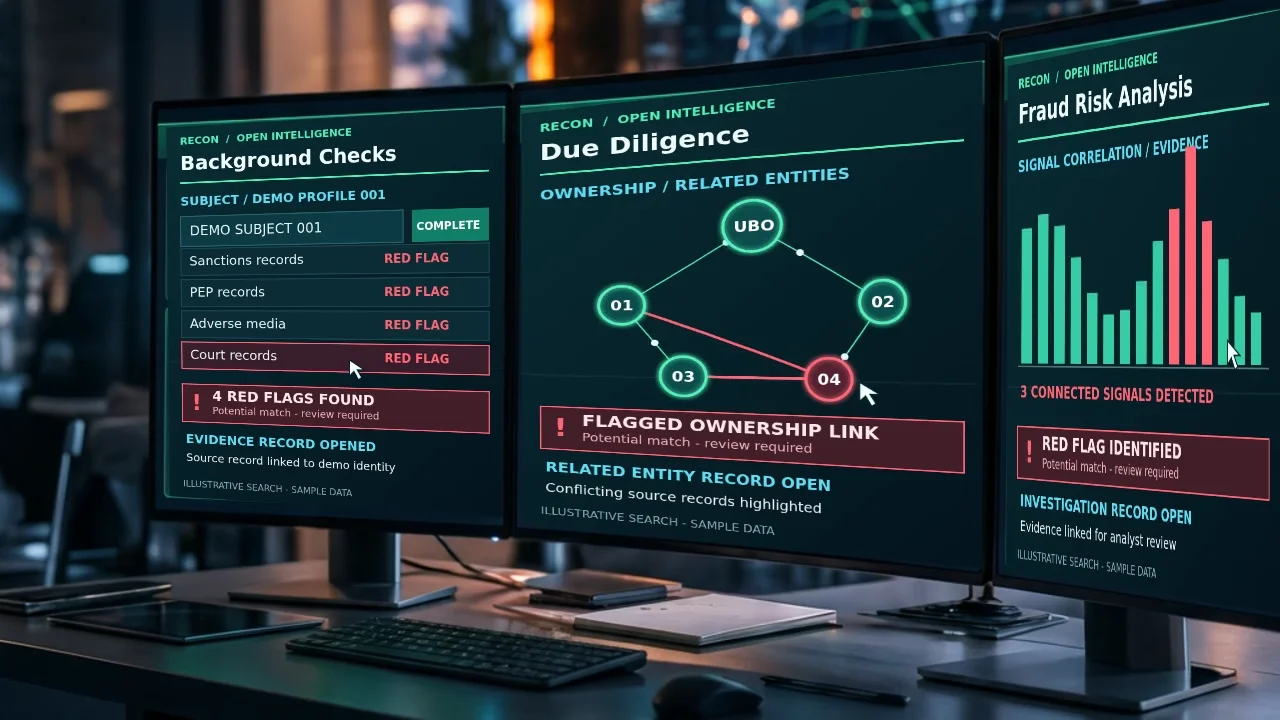
- Background Checks
- Due Diligence
- Fraud Risk Analysis
People · Technology · Processes
RECON / OPEN INTELLIGENCE
The Most Powerful Solution for Background Checks, Due Diligence, and Fraud Risk Analysis in the World.
Recon is Lyon & Fiurex's open-source intelligence offering. Scoped, analyst-led research on public sources turns people and companies into resolved identities and a cited report for your decision.
- Analyst-led public-source research
- Identity resolution
- Cited report
- ISO 9001
- ISO 27001
- ISO 37001
- EN / ES / FR
Offensive Cybersecurity Consultancy and Data Protection, specialised in SMBs and Enterprise (MSSP)
Start here
Select the size of your company
Each path leads to a page built for that device range.
Our Approach
A phased program for every company
We walk with you from an initial security audit all the way to full-time security operations — scoped to your company size.
Select a phase to read its detail
Establish a baseline of controls and compliance with local and international regulations.
We review or take over your IT operation: tools, configuration, and processes.
Access control inside and outside the corporate network, and protection across every device.
You cannot protect what you cannot see. We deploy visibility, monitoring, and detection.
Continuously discover, prioritize, and remediate vulnerabilities.
We secure your cloud environments and embed security across the entire development lifecycle: protection for AWS, Azure, and GCP, and end-to-end DevSecOps practices.
We protect your company's sensitive information and ensure privacy compliance: data loss prevention, encryption, and key management.
Production-ready incident response and disaster recovery capability.
We put your defenses to the test — pentesting, security testing, and team awareness — to prove they hold and keep them sharp.
Phase 0 — Security Audit
Establish a baseline of controls and compliance with local and international regulations.
About Lyon & Fiurex
Offensive cybersecurity and data protection, specialized in SMBs
Lyon & Fiurex is an offensive cybersecurity and data-protection consultancy specialized in small and medium businesses, part of the REDGOLD Holding group. We combine people, technology, and processes to reduce risk in a measurable way.
Anti-Bribery Commitments & Ethical Conduct within Lyon & Fiurex LLC Group and all its Partners
Prohibit bribery, extortion, collusion, facilitation payments, improper commissions, inappropriate gifts, undeclared conflicts of interest, and any act contrary to professional ethics.
Comply with applicable anti-bribery laws and obligations, as well as the contractual and integrity requirements demanded by clients and partners.
Promote ethical conduct across all our services — security audits, vulnerability management, penetration testing and security assurance, threat detection and monitoring (SOC), cyber threat intelligence (CTI), digital forensics, incident response and DRP, OSINT, due diligence, investigations, data protection and privacy, recruitment and selection, training, and business relationships — preventing any individual from modifying, deleting, excluding, or tampering with results, evidence, or information for personal gain, bribery, or out of malice, and avoiding any manipulation of results, undue bias, or unauthorized use of information.
Protect those who report concerns, suspicions, or breaches related to bribery, corruption, fraud, or unethical conduct in good faith. Protect the confidentiality of reports. The presumption of innocence must also be guaranteed. Conduct investigations of reports under strict confidentiality until conclusive results are available.
Certifications We Have
Our team is backed by world-class certifications across offensive security, GRC, blue team, and more.

CC
Certified in Cybersecurity
ISO 27001 Lead Auditor
ISO 27001 Lead Implementer
ISO 27001 Internal Auditor
ISO 22301 Internal Auditor
ISO 22302 Lead Auditor
ISO/IEC 20000 Internal Auditor
AI Risk Manager Professional
CEH-P
Certified Ethical Hacker (Practical)

CPTS= OSCP+
Certified Penetration Testing Specialist
CWES
Certified Web Exploitation Specialist
CWEE= OSWE
Certified Web Exploitation Expert
CBBH
Certified Bug Bounty Hunter

CompTIA Pentest+
CompTIA Security+
Offensive Security
eJPT
eLearnSecurity Junior Penetration Tester
CJCA
Certified Junior Cybersecurity Associate
CWPE
Certified Wifi Pentesting Expert
Red Teaming

Burp Suite Certified Practitioner
CTIGA
Certified Threat Intelligence & Governance Analyst

SOC Analyst I
SOC Analyst II
Security Engineer
DevSecOps
Attacking and Defending AWS
CompTIA Cloud+
CompTIA A+
ITIL 4 Foundation
Agile Leader Professional
Scrum Advanced Professional
Artificial Intelligence Expert
Cyber Human Resources
Trained cybersecurity talent, ready to embed
We keep an extended bench of well-trained cybersecurity professionals at your disposal — from Penetration Testers to ISO 27001, NIST, PCI DSS, SOX, and ICS/SCADA auditors.
See the positions- Penetration Tester
- Security Engineer
- SOC Tier I / II
- Threat Analyst
- Cloud Security
- DevSecOps Engineer
- ISO 27001 Auditor
- NIST Auditor
- PCI DSS Auditor
- SOX Auditor
Exclusive Research
The Dirty Secrets of OSINT Vendors
Same tools. Different risks. All the facts. Source-verified. Publicly documented. No spin.
Read the full investigation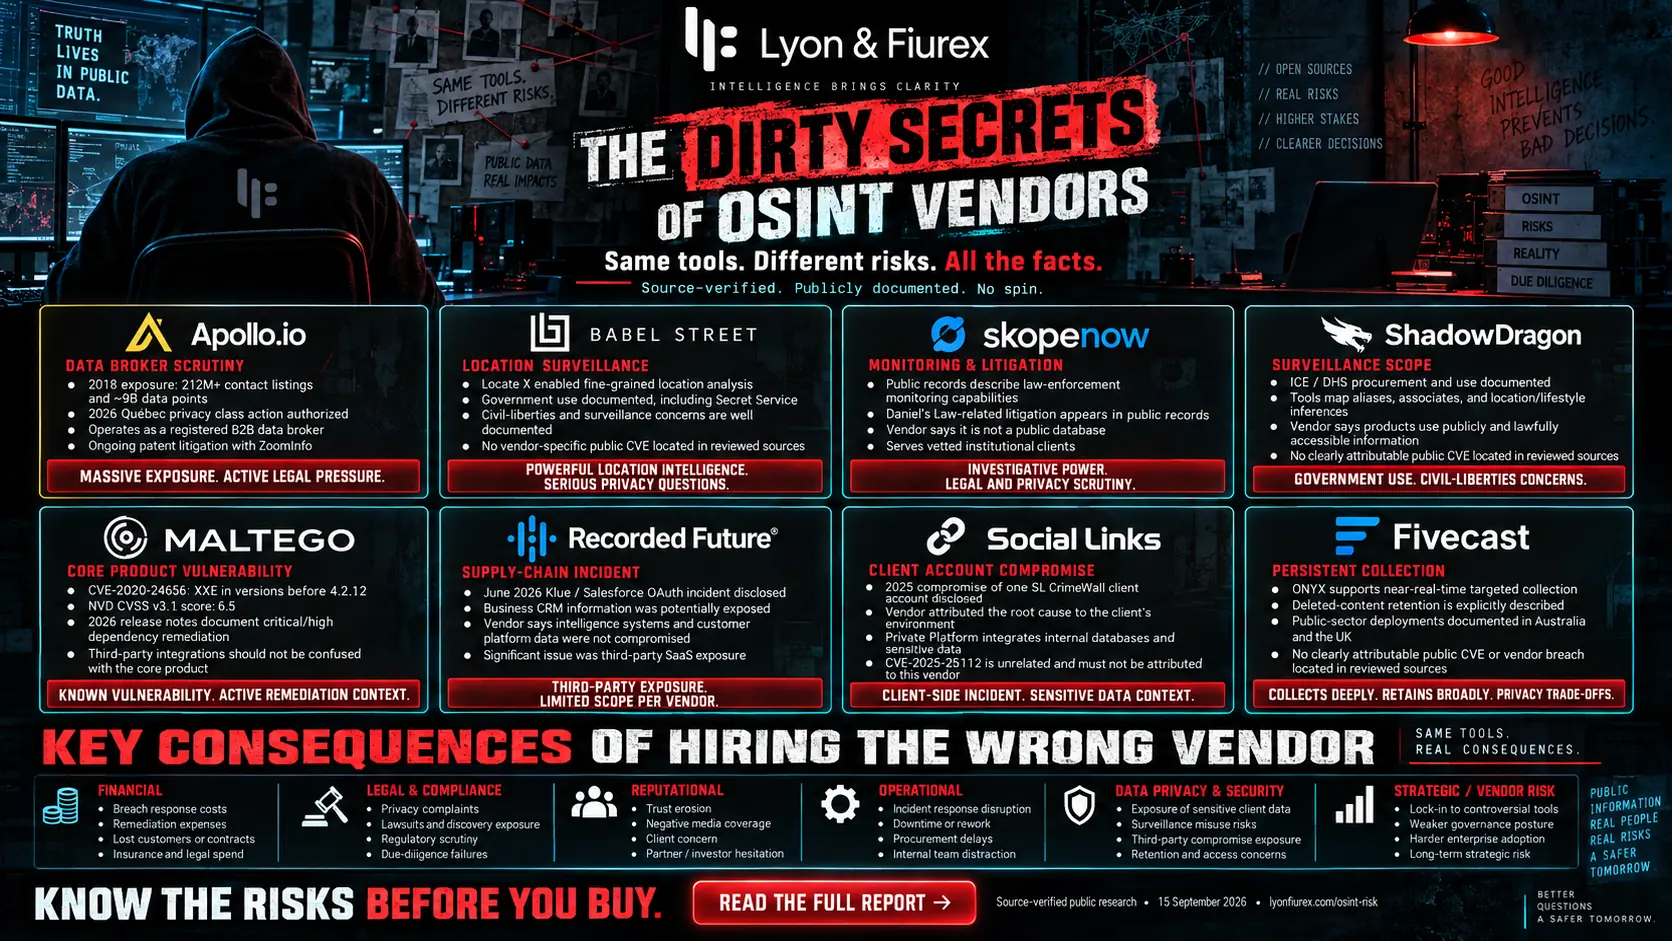
Free Tool
Free OSINT — Open-source intelligence, at no cost
Access our free OSINT platform to discover publicly available information about domains, emails, IPs, and more. No credit card, no commitment.
Get free accessReady to secure your enterprise?
Talk to our advisory team about custom training and consulting.
- Reply from the advisory team
- Scoped to your device range
- No obligation to continue